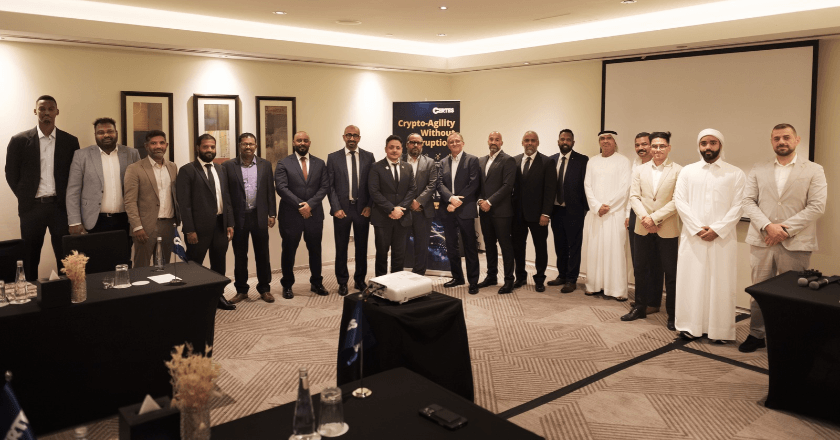
Held alongside the CISO50 and Future Security Awards 2026, the Dubai roundtable explored data-centric security, quantum readiness and protecting sensitive information after systems are compromised.
Protecting sensitive data after a breach requires security strategies that extend beyond preventing unauthorised access. Organisations must consider how to keep intercepted information unusable, strengthen control over data flows and prepare for quantum-related risks without disrupting existing operations.
Examining how CISOs can achieve these objectives was the focus of the “Devalue the stolen data” roundtable, hosted by TahawulTech.com with Certes on 15 October 2026 at The Westin Dubai Mina Seyahi Beach Resort & Marina. Held alongside the CISO50 and Future Security Awards 2026, the private discussion explored data-centric protection, crypto-agility and practical approaches to securing information across legacy, hybrid and cloud environments.
The roundtable examined the shift from perimeter-focused defence towards protection that follows the data. Its agenda centred on the consequences of compromised credentials, applications and infrastructure, and the need to reduce the value of information that attackers manage to steal.
Rami Nehme, Managing Director – META, Certes, identified the gap between traditional cyber defences and the protection of sensitive data itself as one of the strongest concerns raised during the roundtable.
“Security leaders emphasised the challenges of achieving post-quantum readiness across complex legacy, hybrid, and cloud environments, without disrupting critical business operations,” Nehme said.
He also highlighted crypto-agility: the ability to adapt cryptographic protection as threats, regulations and standards evolve, without repeatedly replacing infrastructure or modifying applications.
The discussion covered the adequacy of existing encryption and key-management strategies, including how organisations control access to sensitive data across legacy systems, cloud platforms, hybrid infrastructure and third-party environments. Customer-controlled key management and policy enforcement formed part of the examination of how protection can extend across these interconnected environments.
Quantum readiness provided another focus. The “harvest now, decrypt later” threat describes the risk of attackers collecting encrypted information with the intention of decrypting it when more powerful computing capabilities become available. For organisations holding information that must remain confidential for many years, this makes the lifespan of sensitive data an important consideration in security planning.
Simon Pamplin, CTO, Certes, said, “CISOs don’t need to replace existing infrastructure to make stolen data unusable. The priority is to protect the data itself, not just the network or perimeter. Apply policy-driven, cryptographic protection to data in motion across cloud, WAN, edge, OT and legacy environments, with controls that prevent unauthorised movement and access. At the same time, build crypto-agility: the ability to change cryptographic algorithms and key management as post-quantum standards evolve.
“Quantum readiness is not simply deploying PQC; it requires evidence that implementations work as intended. Protect data today, while preparing to adapt tomorrow.”
For UAE organisations, Nehme translated these concerns into practical priorities: identifying critical data flows, implementing advanced encryption and applying granular crypto-segmentation to minimise exposure and limit the impact of a breach.
“The priority should be adopting a data-centric security approach, where protection follows the data regardless of the network, application, or infrastructure it travels through,” he said.
Explaining Certes’ approach, Nehme pointed to Layer 4 payload encryption, crypto-segmentation and centrally managed cryptographic policies. He said these capabilities enable organisations to protect sensitive data in transit across complex environments without requiring fundamental changes to existing applications or infrastructure, while supporting a more agile transition towards quantum-safe cryptography.
Board and regulatory accountability also featured in the agenda. Beyond deploying controls, security leaders need to demonstrate how those controls protect important information and provide evidence that can support audits and risk oversight. Measurable protection therefore connects technical implementation with the wider governance responsibilities of the CISO.
Nehme’s closing observation captured the discussion’s focus on reducing the consequences of a breach: “Ultimately, the measure of cyber resilience should not only be whether an attacker can breach your defences, but whether the data they manage to intercept has any value to them.”
Source: Tahawul Tech